by Ron Samson | Sep 13, 2026 | Cybersecurity, SIEM and Log Management, SOC as a Service
Log Retention Is an Investigation Decision, Not a Storage Setting Most organizations discover their log-retention problem during an incident. A ransomware investigation requires authentication history from three months earlier. Legal asks for evidence of unusual...
by Ron Samson | Sep 10, 2026 | Cybersecurity, SOC as a Service
The SOC staffing question is not simply “build or buy” Security leaders rarely begin with a clean decision between an internal security operations center and an outsourced provider. The immediate problem is usually more practical: alerts are accumulating, endpoint...
by Ron Samson | Sep 7, 2026 | SOC as a Service
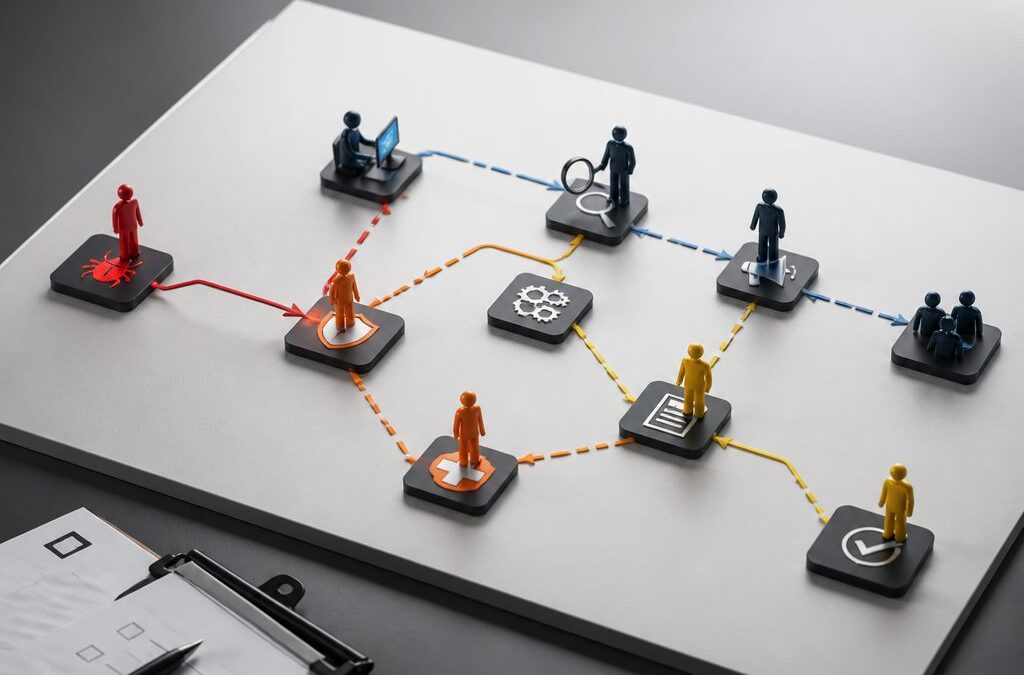
An escalation process is only real when it has been exercised Most organizations have an incident response plan, an on-call roster, and a collection of security tools. Far fewer know whether those components work together under pressure. A documented escalation path...
by Ron Samson | | Email Security, SOC as a Service, Threat Detection and Response
A Microsoft 365 takeover is a financial incident, not just an identity incident A business email compromise (BEC) event moves quickly because the attacker is already operating from a trusted identity. Once they control a Microsoft 365 mailbox, they can read invoice...
by Ron Samson | Aug 25, 2026 | SOC as a Service
The difference between advertised and operational coverage Buying SOC as a Service is not a checklist exercise. Providers can present similar dashboards, certifications, and technology logos, yet their operating models may produce radically different outcomes when a...
